Close

Track: IT & Infrastructure

Tue 03
11:00h
Side Event | Side Event AI, identity and trust in the digital environment IT & Infrastructure

Opening Keynote: The Quantum-Safe Transition
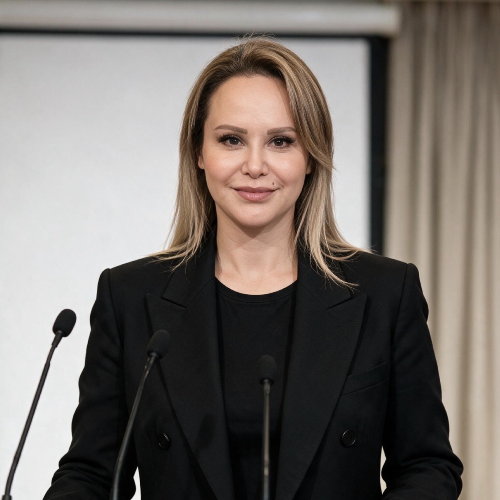
Magda Chelly
Magda Chelly Independent CISO and Cyber Risk Advisor Speaker

2026-11-03 11:00 2026-11-03 11:30 Europe/Madrid Opening Keynote: The Quantum-Safe Transition
Quantum from the CISO's chair: you can't migrate what you can't see
For most security leaders, the quantum threat won't arrive as a mathematics problem. It arrives as three practical questions: which systems use public-key cryptography, who controls the libraries and hardware behind them, and what the move will cost. This talk treats post-quantum migration from the CISO's side of the table.
It starts by reframing "harvest now, decrypt later" as a data shelf-life question: which of your data must still be confidential in ten or fifteen years, and where does it travel today? It then turns Mosca's inequality into an entry a risk committee can read, with an owner, a timeline and a residual exposure. Drawing on the BIS Project Leap trials in the TARGET2 payment system, it shows why migration is a dependency and performance problem, not a cipher swap. It closes with what a board will realistically fund this year: cryptographic inventory, vendor commitments in contracts, and crypto-agility built into every new system

Level 0 - Room 2.2
Tue 3
11:00h - 11:30h Level 0 - Room 2.2 Public Access
11:00h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Quantum-Safe Threat: Standards and Regulations
Schedule
11:00h - 11:30h
Opening Keynote: The Quantum-Safe Transition
Magda Chelly
Magda Chelly Independent CISO and Cyber Risk Advisor Speaker
11:30h - 12:15h
Round Table: What technologies can help mitigate the quantum threat? How can businesses adopt them?
Victor Canivell
Victor Canivell Qilimanjaro President and Co-Founder Speaker
Vanesa Díaz
Vanesa Díaz Luxquanta QKD expert Speaker
Carlos Abellan
Carlos Abellan Quside PQC expert Speaker
Natalia Gómez
Natalia Gómez CTTI Director of Strategy and Planning for Digital Infrastructure Speaker
Jordi Mur
Jordi Mur Emerging Technologies, Quantum & Cybersecurity Expert Moderator
12:15h - 13:00h
Round Table: Preparing for the Quantum-Safe Transition – The End-User Perspective
Manuel García-Cervigón
Manuel García-Cervigón Nestlé Strategic Product Portofolio Architect, IT Security & Compliance Speaker
Joan Puig
Joan Puig Banc Sabadell CISO Speaker
Pau Serra
Pau Serra CaixaBank Tech Security Architect Speaker
Isart Canyameres
Isart Canyameres Cybersecurity Agency of Catalonia Head of the Innovation Unit Moderator
13:00h - 13:15h
Closing Remarks
Magda Chelly
Magda Chelly Independent CISO and Cyber Risk Advisor Speaker

2026-11-03 11:00 2026-11-03 13:15 Europe/Madrid Quantum-Safe Threat: Standards and Regulations Quantum-Safe Threat: Standards and Regulations
As part of this side event, participants will have the opportunity to visit the Barcelona Supercomputing Center free of charge. Registration here
Level 0 - Room 2.2
Tue 3
11:00h - 13:15h Level 0 - Room 2.2 Public Access
10:45h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

Defending at machine speed: From trusting what we see to trusting what we can prove
Bryan Lopez
Bryan Lopez Mastercard Senior Vice President and Field CISO, Commercial Speaker

2026-11-03 10:45 2026-11-03 11:10 Europe/Madrid Defending at machine speed: From trusting what we see to trusting what we can prove
As cyber threats evolve, CISOs need to understand not only where risk exists, but how it translates into business and financial impact. This talk explores how connecting cyber, fraud and identity intelligence can create a more complete picture of risk, helping organizations identify threats earlier, focus on what matters most and strengthen resilience.

Auditorium I
Tue 3
10:45h - 11:10h Auditorium I Full Congress Pass
10:45h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

When AI becomes the adversary: The new race between cyber attackers and defenders
James Burchell
James Burchell Crowdstrike Sales Engineering Manager Speaker

2026-11-03 10:45 2026-11-03 11:10 Europe/Madrid When AI becomes the adversary: The new race between cyber attackers and defenders Agentic AI is reshaping cyberattacks, enabling adversaries to move beyond AI-assisted operations toward autonomous intrusions. CrowdStrike's latest threat research reveals real-world examples of AI agents executing complex attack tasks with minimal human direction or intervention. Drawing on frontline adversary intelligence, this keynote explores the rise of the agent-state and the new challenges it creates for defenders. Learn how organisations can rethink their defences to counter AI-driven attacks, combining human expertise, adversary intelligence, and AI-powered security to stay ahead. Auditorium II
Tue 3
10:45h - 11:10h Auditorium II Full Congress Pass
13:40h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

From 840 days to 1.6: Rebuilding application security for the Frontier-AI era
Daniela da Cruz
Daniela da Cruz Checkmarx Vice President of Artificial Intelligence Speaker

2026-11-03 13:40 2026-11-03 14:10 Europe/Madrid From 840 days to 1.6: Rebuilding application security for the Frontier-AI era
In 2018, the median time to exploit a disclosed vulnerability was 840 days. Today it is 1.6, and frontier AI is pushing that toward minutes. At the same time, AI is writing a growing share of production code, adding new vulnerabilities on top of unresolved backlogs. European regulators have taken notice: from DORA and the EU AI Act to the ECB’s requirement that significant banks submit a cyber-resilience action plan by 31 October 2026, “should have” has become “must have”.
This session looks at what that shift means for security and engineering leaders, in banking and beyond. We will examine why AI-only security (fast, but probabilistic) and traditional AppSec (reliable, but slow and noisy) each fall short, and how a hybrid model, combining deterministic detection with multi-model AI reasoning, can surface vulnerabilities that rules alone miss while cutting false-positive noise. We’ll then follow findings through to action: triage prioritised by attackability rather than severity, automated remediation, and the governance needed to keep humans in control.
Attendees will leave with a practical Capture, Eliminate, Govern framework and a checklist for turning a regulatory action plan into day-to-day engineering practice.
Auditorium II
Tue 3
13:40h - 14:10h Auditorium II Full Congress Pass
16:55h
Conference | Congress Systemic, cyber-physical and supply chain resilience IT & Infrastructure

From smart cities to cyber-resilient cities. How Greater Paris is helping municipalities prepare for cyber
Geoffroy Boulard
Geoffroy Boulard Greater Paris Metropolis Vice-President for Communication and Digital Innovation Speaker

2026-11-03 16:55 2026-11-03 17:20 Europe/Madrid From smart cities to cyber-resilient cities. How Greater Paris is helping municipalities prepare for cyber As cities become increasingly digital, cybersecurity is a growing concern for local governments. This session will explore the main challenges faced by municipalities and present how the Greater Paris Metropolis supports local authorities in strengthening their cyber resilience. Through initiatives such as the CYBIAH programme, a municipal Bug Bounty scheme and REMPART, a cyber crisis simulation exercise developed with ANSSI, the session will showcase practical tools and collaborative approaches to help cities better anticipate, prevent and respond to cyber threats. Auditorium II
Tue 3
16:55h - 17:20h Auditorium II Full Congress Pass
12:30h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

Simplifying AI complexity: How to survive in the post-Mythos era
Román Vargas Sierra
Román Vargas Sierra Cisco Cybersecurity Sales Specialist Speaker

2026-11-03 12:30 2026-11-03 12:55 Europe/Madrid Simplifying AI complexity: How to survive in the post-Mythos era
Artificial intelligence has moved out of the lab and into the very heartbeat of our society. But with unprecedented speed comes unprecedented complexity. In the post-Mythos era, AI is not just a productivity tool; it is an active, autonomous participant in our digital ecosystems.
For many organizations, managing this revolution has turned into an operational labyrinth of fragmented tools, blind spots and emerging security risks. 
How do we embrace the immense power of AI without losing control of our critical systems?
Join this session for an insightful, no-nonsense roadmap on how leaders can strip away the noise, master AI complexity and build digital environments that are resilient, transparent and ready for tomorrow.
Auditorium I
Tue 3
12:30h - 12:55h Auditorium I Full Congress Pass
17:00h
Side Event | Side Event AI, identity and trust in the digital environment CISOs & Security Leader IT & Infrastructure

Deepfakes & Spoofing: When SMS and Voice Cannot Be Trusted
Xavier Álvarez
Xavier Álvarez Merabytes Director de Operaciones Speaker

#Security, #Spoofing

2026-11-03 17:00 2026-11-03 17:30 Europe/Madrid Deepfakes & Spoofing: When SMS and Voice Cannot Be Trusted Today, threat actors can send calls and SMS from any number, with any text and voice, seamlessly impersonating bank clients and providers. We’ll cover critical defenses, including why you should adopt RCS, how to implement rotating voice security keys, and the importance of real-world deepfake simulations. Networking Hub
Tue 3
17:00h - 17:30h Networking Hub Public Access
16:30h
Side Event | Side Event AI, identity and trust in the digital environment CISOs & Security Leader IT & Infrastructure

Nobody Reads 40,000 Vulnerability Findings
Gerardo Prieto
Gerardo Prieto The Mill Adventure CISO Speaker

#HumanInTheLoop, #Remediation

2026-11-03 16:30 2026-11-03 17:00 Europe/Madrid Nobody Reads 40,000 Vulnerability Findings Handing the backlog to a chain of AI agents — and knowing when to stop and ask a human. Detection was never the bottleneck. Triage, ownership, chasing and retesting are. This session walks through an agentic pipeline that takes a finding — whether it came from a cloud scanner, a SAST tool, an endpoint agent or a pentest report — all the way to a verified fix. Contextual severity scoring, one agent independently checking another's work, and the hard part: knowing when the automation is confident and when a human still has to decide. Networking Hub
Tue 3
16:30h - 17:00h Networking Hub Public Access
16:20h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

New threat landscape and challenges in the age of Frontier AI
Joan Ruiz
Joan Ruiz Fortinet Systems Engineer Manager Speaker

2026-11-03 16:20 2026-11-03 16:45 Europe/Madrid New threat landscape and challenges in the age of Frontier AI In this talk we will discuss current state of the art and landscape of emerging threats due to the progress of frontier ai models and we'll introduce Fortinet layered security approach to  fight against it Auditorium I
Tue 3
16:20h - 16:45h Auditorium I Full Congress Pass
11:00h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience Compliance & Data Protection IT & Infrastructure

Cómo gestionar dependencias en proyectos industriales complejos
María Dolores Trapero
María Dolores Trapero Elecnor Sistemas Responsable de Centro de Ciberseguridad y redes IT/OT Speaker

2026-11-03 11:00 2026-11-03 11:20 Europe/Madrid Cómo gestionar dependencias en proyectos industriales complejos text Networking Hub
Tue 3
11:00h - 11:20h Networking Hub Public Access
10:40h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience CISOs & Security Leader IT & Infrastructure

El papel del fabricante en la ciberresiliencia industrial
César Delgado
César Delgado Rockwell Automation Cybersecurity Business Development Speaker

2026-11-03 10:40 2026-11-03 11:00 Europe/Madrid El papel del fabricante en la ciberresiliencia industrial text Networking Hub
Tue 3
10:40h - 11:00h Networking Hub Public Access
10:20h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience CISOs & Security Leader IT & Infrastructure

¿Qué ocurre cuando falla un tercero tecnológico crítico?
Oscar López
Oscar López Grupo Agrolimen Cybersecurity & IT Governance Manager Speaker

2026-11-03 10:20 2026-11-03 10:40 Europe/Madrid ¿Qué ocurre cuando falla un tercero tecnológico crítico? text Networking Hub
Tue 3
10:20h - 10:40h Networking Hub Public Access
10:00h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience Compliance & Data Protection CISOs & Security Leader IT & Infrastructure

Ciberresiliencia en la cadena de suministro industrial
Schedule
10:00h - 10:20h
Apertura: la cadena de suministro industrial ya no es una cadena
José Valiente
José Valiente Centro de Ciberseguridad Industrial (CCI) Director General Speaker
10:20h - 10:40h
¿Qué ocurre cuando falla un tercero tecnológico crítico?
Oscar López
Oscar López Grupo Agrolimen Cybersecurity & IT Governance Manager Speaker
10:40h - 11:00h
El papel del fabricante en la ciberresiliencia industrial
César Delgado
César Delgado Rockwell Automation Cybersecurity Business Development Speaker
11:00h - 11:20h
Cómo gestionar dependencias en proyectos industriales complejos
María Dolores Trapero
María Dolores Trapero Elecnor Sistemas Responsable de Centro de Ciberseguridad y redes IT/OT Speaker
11:20h - 12:00h
Panel – ¿Quién controla realmente el riesgo de la cadena de suministro industrial?
Oscar López
Oscar López Grupo Agrolimen Cybersecurity & IT Governance Manager Speaker
César Delgado
César Delgado Rockwell Automation Cybersecurity Business Development Speaker
Pablo  Carmona
Pablo Carmona Preventa de Redes y Ciberseguridad OT/IT Speaker
Joan Figueras
Joan Figueras Coordinador de CCI en Cataluña Speaker
Maite Arcos
Maite Arcos Fundación ESYS Directora Moderator

2026-11-03 10:00 2026-11-03 12:00 Europe/Madrid Ciberresiliencia en la cadena de suministro industrial La resiliencia industrial ya no depende únicamente de proteger los activos propios, sino de comprender y gobernar las dependencias tecnológicas que sostienen la operación. Este side event aborda la cadena de suministro desde cuatro perspectivas complementarias: operador industrial, fabricante, ingeniería y gobierno del riesgo. Analizaremos qué ocurre cuando falla un tercero tecnológico crítico, cómo diseñar productos y arquitecturas capaces de resistir, y cómo gestionar dependencias en proyectos industriales complejos. La sesión culminará con un panel sobre quién controla realmente el riesgo de la cadena de suministro, poniendo el foco en responsabilidad compartida, visibilidad, alternativas, capacidad de respuesta y continuidad operativa. Networking Hub
Tue 3
10:00h - 12:00h Networking Hub Public Access
10:00h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience CISOs & Security Leader IT & Infrastructure

Apertura: la cadena de suministro industrial ya no es una cadena

José Valiente
José Valiente Centro de Ciberseguridad Industrial (CCI) Director General Speaker

2026-11-03 10:00 2026-11-03 10:20 Europe/Madrid Apertura: la cadena de suministro industrial ya no es una cadena text Networking Hub
Tue 3
10:00h - 10:20h Networking Hub Public Access
16:20h
Conference | Congress Cybersecurity as a strategic business and reputational risk IT & Infrastructure

Improve security posture: Start with your endpoints
Juan José González
Juan José González NinjaOne Level 2 Solutions Engineer Speaker

2026-11-03 16:20 2026-11-03 16:45 Europe/Madrid Improve security posture: Start with your endpoints
Many organizations continue to invest heavily in advanced cybersecurity solutions in efforts to better defend against attacks that are not only increasing in frequency but also becoming more complex and difficult to detect. However, the importance of good cyber hygiene, starting with the endpoint, is often overlooked.
NinjaOne consolidates workflows, reduces silos, and provides a single source of truth for all your security and endpoint data.
Join NinjaOne's Solutions Engineer Juan José González as he demonstrates the power and simplicity of the NinjaOne platform and how it can enable you to achieve these benefits:
Detect and respond to threats faster with real-time visibility and control over your entire IT environment.
Harden endpoints by removing unnecessary software and minimizing your attack surface through automated device configuration at scale.
Make sure systems are always secure and up to date with automated patch management.
Recover quickly in the event of an attack with secure, cloud-based backup.
Auditorium II
Tue 3
16:20h - 16:45h Auditorium II Full Congress Pass
15:10h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

Stop managing remote access. Start governing vendors
Michael Ferdinandsen
Michael Ferdinandsen Secomea CEO & President Speaker

#AccessGovernance, #AISecurity, #CyberPhysicalResilience, #IdentityGovernance, #PrivilegedAccess, #SecureRemoteAccess

2026-11-03 15:10 2026-11-03 15:35 Europe/Madrid Stop managing remote access. Start governing vendors Third-party access has become one of the biggest cybersecurity and compliance challenges in modern manufacturing. As vendor ecosystems grow and regulations such as NIS2 raise accountability, manufacturers need more than secure connectivity. They need visibility, governance, and control. Discover why third-party access management is emerging as a strategic OT capability and how purpose-built Secure Remote Access enables secure collaboration without compromising productivity. Auditorium I
Tue 3
15:10h - 15:35h Auditorium I Full Congress Pass
11:20h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

Your agents will inherit your blind spots: Context before autonomy in the integrated SOC
Charalambos Ioannides
Charalambos Ioannides ClearSkies™ Sales Engineering Manager Speaker

2026-11-03 11:20 2026-11-03 11:45 Europe/Madrid Your agents will inherit your blind spots: Context before autonomy in the integrated SOC

Every agentic SOC demo works, because every demo environment has perfect context. Yours does not. An alert carries almost none of what is needed to judge it: who the identity is, how critical the asset is, what depends on it, whether a change window is open. Analysts assemble that context by asking people. An agent has nobody to ask, and when context is missing it does not stop, it reasons around the gap and answers confidently anyway.

Auditorium II
Tue 3
11:20h - 11:45h Auditorium II Full Congress Pass
15:45h
Conference | Congress Cybersecurity as a strategic business and reputational risk IT & Infrastructure

Assume breach, prepare for recovery: Why data resilience is mandatory for business survival
Miguel Tena Martin
Miguel Tena Martin Object First Field Sales Engineer Speaker

#BusinessContinuity, #CyberResilience, #DataProtection, #DataResilience, #DisasterRecovery, #Ransomware, #Recovery

2026-11-03 15:45 2026-11-03 16:10 Europe/Madrid Assume breach, prepare for recovery: Why data resilience is mandatory for business survival
Zero Trust teaches us to assume that there’s a breach, but what’s the worst that could happen when there is a breach? And how do you mitigate against that?
Join Miguel Tena, Object First Field Sales Engineer as he discusses why data resilience is critical in the evolving cybersecurity landscape and what that means in practice. Leveraging insights from research on data protection and ransomware trends, Miguel will explore how organisations can prepare for the worst-case scenario: where a cybercriminal has access to all passwords and secrets. Meeting regulatory and cyberinsurance requirements and, ultimately, guaranteeing business survival mean this is no longer ‘just’ an IT topic, it’s a board-level imperative.
Auditorium II
Tue 3
15:45h - 16:10h Auditorium II Full Congress Pass
14:35h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

Securing AI agents

Roger Gallego
Roger Gallego Delinea Iberia Sales Manager Speaker

#AccessGovernance, #AIAgents, #AISecurity, #Authorization, #IdentityGovernance, #PrivilegedAccess, #RuntimeAuthorization

2026-11-03 14:35 2026-11-03 15:00 Europe/Madrid Securing AI agents
Chasing every agent identity in our organizations doesn't scale. We must implement runtime authorization, which enforces policy at the point of action.
Agents are running on standing credentials issued to people, not to systems. Vault them and replace standing access with just-in-time access.
Auditorium II
Tue 3
14:35h - 15:00h Auditorium II Full Congress Pass
15:45h
Conference | Congress Cybersecurity as a strategic business and reputational risk IT & Infrastructure

Are you okay, Internet? The state of the internet in 2026
Martijn Grooten
Martijn Grooten Censys Principal Security Researcher Speaker

#AttackSurface, #CyberRisk, #InfrastructureSecurity, #InternetExposure, #InternetSecurity

2026-11-03 15:45 2026-11-03 16:10 Europe/Madrid Are you okay, Internet? The state of the internet in 2026 In this presentation, Censys researcher Martijn Grooten walks through interesting findings from the 2026 Censys State of the Internet report and will answer questions such as: what trends do we see when it comes to Internet-connected services? Who are the major players? What are the vulnerabilities that should concern us? How is the rapid adoption of AI affecting the Internet map. Auditorium I
Tue 3
15:45h - 16:10h Auditorium I Full Congress Pass
Wed 04
14:35h
Conference | Congress Cybersecurity as a strategic business and reputational risk IT & Infrastructure

PHP2Shell: Why the patch isn’t the fix, and the playbook for the next one
Greg Olmstead
Greg Olmstead Nubelo Engineering Co-Founder Speaker

2026-11-04 14:35 2026-11-04 15:00 Europe/Madrid PHP2Shell: Why the patch isn’t the fix, and the playbook for the next one A vendor-agnostic look at PHP2Shell (CVE-2026-109618/109619), from early leak to patch to in-the-wild exploitation. We'll cover why it bypasses application-layer defences, why old PHP versions with no official fix leave public-sector and smart-city estates exposed, and why leaked memory means rotating credentials is part of the response, not an afterthought. Attendees leave with a practical playbook: asset discovery, prioritising unsupported versions, rotating secrets, and deciding what to do when a disclosure comes out before the fix. Auditorium I
Wed 4
14:35h - 15:00h Auditorium I Full Congress Pass
15:45h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

The absent perimeter: Why modern SOCs must defend the cognitive layer
Xavier Martí-Renom
Xavier Martí-Renom Sirt Head of Intellectual Property & Business Development Speaker

2026-11-04 15:45 2026-11-04 16:10 Europe/Madrid The absent perimeter: Why modern SOCs must defend the cognitive layer As modern Security Operations Centers (SOCs) automate their operations using AI with autonomous capabilities (agentic AI), attackers are bypassing technical defenses by directly exploiting the minds of authorized users through advanced social engineering techniques. This trend reveals a critical gap in the "Zero Trust" model: while this model validates identities and devices, it fails to detect when a user is acting under psychological manipulation. Cognitive security can no longer be limited to traditional awareness training; it must be integrated as an operational capability within the SOC and the Security Incident Response Team (SIRT). In this session, we will examine how incident response teams can incorporate cognitive defense into their workflows, and why corporate culture and context—just as much as technical telemetry—are crucial for mitigating these types of attacks. Auditorium II
Wed 4
15:45h - 16:10h Auditorium II Full Congress Pass
14:15h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Fireside chat: Cross sector collaboration and cyber defence capabilities for critical infrastructures: Supply chains, subsea cables and resilient compute
Holger Spohn
Holger Spohn North Atlantic Treaty Organisation Principal Engineer (Advanced Cyber Defence Principles) Speaker
Ulrich Seldeslachts
Ulrich Seldeslachts LSEC Leaders in Security CEO Speaker

2026-11-04 14:15 2026-11-04 14:45 Europe/Madrid Fireside chat: Cross sector collaboration and cyber defence capabilities for critical infrastructures: Supply chains, subsea cables and resilient compute
Modern critical infrastructure resilience extends far beyond corporate IT networks. Today’s smart transport, aviation and maritime logistics depend directly on fragile global foundations: subsea data cables, specialized semiconductor pipelines, cloud compute nodes and dual use. In an era of heightened geopolitical friction and hybrid threats, disruptions to these shared backbones pose systemic risks to European security and economic continuity.
In this high level fireside chat, Holger Spohn (NATO) and Ulrich Seldeslachts (LSEC) bridge cyber defense with commercial and industrial reality. Following a 15 minute framing of the strategic landscape, highlighting subsea cable vulnerabilities, compute dependency and dual use supply chain resilience, the session opens into an interactive debate. Holger and Ulrich will challenge the CISOs, transport authorities and critical infrastructure operators in the room to examine their own operational readiness and cross-sector response capabilities under crisis conditions.
Level 1 - Room 2.3
Wed 4
14:15h - 14:45h Level 1 - Room 2.3 Public Access
11:30h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Keynote: ACTI-X: From cyber threat intelligence to action in global travel & critical transport infrastructures
Vincent Rigal
Vincent Rigal Head of Amadeus Application Security Operations Centers Speaker

2026-11-04 11:30 2026-11-04 12:00 Europe/Madrid Keynote: ACTI-X: From cyber threat intelligence to action in global travel & critical transport infrastructures
Introduction to the ACTI-X project - Project vision and architecture - Open-source Cyber Threat Intelligence - STIX/TAXII interoperability - AI-supported analysis and automation - From threat information to operational response
Level 1 - Room 2.3
Wed 4
11:30h - 12:00h Level 1 - Room 2.3 Public Access
11:00h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Keynote: Securing Catalonia’s critical transport and logistics: Regional cyber threat intelligence, sector coordination and the role of the Agència
Manel Garcia
Manel Garcia Agència de Ciberseguretat de Catalunya Head of Information Security Speaker

2026-11-04 11:00 2026-11-04 11:30 Europe/Madrid Keynote: Securing Catalonia’s critical transport and logistics: Regional cyber threat intelligence, sector coordination and the role of the Agència Cybersecurity challenges and incident trends across Catalonia’s strategic transport and maritime ecosystems (Port of Barcelona, Port of Tarragona, airport networks, freight corridors) - Threat intelligence sharing (CTI) between critical operators and public authorities - Operational coordination protocols during large-scale cyber disruptions - The role and roadmap of the Agència de Ciberseguretat de Catalunya in safeguarding regional essential services under NIS2. Level 1 - Room 2.3
Wed 4
11:00h - 11:30h Level 1 - Room 2.3 Public Access
10:20h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Opening Keynote: The cyber threat landscape for the transport sector
Marcos Gómez
Marcos Gómez INCIBE - Instituto Nacional de Ciberseguridad CISO & Deputy Director of Corporate Security Speaker

2026-11-04 10:20 2026-11-04 10:45 Europe/Madrid Opening Keynote: The cyber threat landscape for the transport sector Current and Emerging cyber threats - Increasing dependency on connected and digital infrastructures - Aviation and maritime transport as critical infrastructure - From ransomware to supply-chain and hybrid threats Level 1 - Room 2.3
Wed 4
10:20h - 10:45h Level 1 - Room 2.3 Public Access
10:00h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Barcelona Smart Transportation & Maritime Cyber Resilience Forum
Schedule
10:00h - 10:15h
10:15h - 10:20h
Welcome and opening remarks
Ulrich Seldeslachts
Ulrich Seldeslachts LSEC Leaders in Security CEO Speaker
10:20h - 10:45h
Opening Keynote: The cyber threat landscape for the transport sector
Marcos Gómez
Marcos Gómez INCIBE - Instituto Nacional de Ciberseguridad CISO & Deputy Director of Corporate Security Speaker
11:00h - 11:30h
11:30h - 12:00h
Keynote: ACTI-X: From cyber threat intelligence to action in global travel & critical transport infrastructures
Vincent Rigal
Vincent Rigal Head of Amadeus Application Security Operations Centers Speaker
12:00h - 13:00h
Roundtable: From port to aircraft and across supply chain – Common cybersecurity and CTI challenges
Nick Saharan
Nick Saharan CSAFI.ORG President Speaker
Vincent Rigal
Vincent Rigal Head of Amadeus Application Security Operations Centers Speaker
Alejandro Manuel Herrera Pérez
Alejandro Manuel Herrera Pérez Port of Algeciras CISO Speaker
Ulrich Seldeslachts
Ulrich Seldeslachts LSEC Leaders in Security CEO Moderator
13:00h - 13:45h
14:15h - 14:45h
Fireside chat: Cross sector collaboration and cyber defence capabilities for critical infrastructures: Supply chains, subsea cables and resilient compute
Holger Spohn
Holger Spohn North Atlantic Treaty Organisation Principal Engineer (Advanced Cyber Defence Principles) Speaker
Ulrich Seldeslachts
Ulrich Seldeslachts LSEC Leaders in Security CEO Speaker
14:45h - 15:00h
Closing remarks and next steps
Ulrich Seldeslachts
Ulrich Seldeslachts LSEC Leaders in Security CEO Speaker

2026-11-04 10:00 2026-11-04 15:00 Europe/Madrid Barcelona Smart Transportation & Maritime Cyber Resilience Forum A strategic forum on cyber resilience across connected transportation and maritime environments. Bringing together transport, port, shipping and cybersecurity perspectives, the programme will explore emerging threats, OT and IT convergence, operational continuity, regulatory expectations and supply-chain dependencies—from connected mobility systems and transport infrastructure to vessels and ports. The goal is to identify practical priorities for securing essential services and strengthening cross-sector collaboration. Level 1 - Room 2.3
Wed 4
10:00h - 15:00h Level 1 - Room 2.3 Public Access
10:45h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

The future of access security in Europe: AI, non-human Identities and digital sovereignty
Alejandro Soret Madolell
Alejandro Soret Madolell Wallix IT & OT Solutions Engineer Speaker

2026-11-04 10:45 2026-11-04 11:10 Europe/Madrid The future of access security in Europe: AI, non-human Identities and digital sovereignty Can Europe truly achieve digital sovereignty without controlling who or what can access its critical systems? This session explores how Privileged Access Management (PAM) is evolving, from securing administrator accounts to managing access for non-human identities and AI agents. Through practical examples, we'll look at the challenges of controlling privileged access and why this is essential for Europe's digital sovereignty. Auditorium II
Wed 4
10:45h - 11:10h Auditorium II Full Congress Pass
16:00h
Side Event | Side Event AI, identity and trust in the digital environment Compliance & Data Protection IT & Infrastructure

Agents that act, humans that respond
José Manuel Tejedor Lloria
José Manuel Tejedor Lloria Global CISO Council Spain Chapter Vice President – Finance Moderator
Eva Puerta Pérez
Eva Puerta Pérez Global CISO Council Spain Chapter Vice President – Academia Speaker
Rubén Cortés Domingo
Rubén Cortés Domingo Global CISO Council Spain Chapter Advisory Board Member Speaker
Xavier Duch
Xavier Duch Global CISO Council Spain Chapter Advisory Board Member Speaker

2026-11-04 16:00 2026-11-04 17:30 Europe/Madrid Agents that act, humans that respond
Artificial intelligence is moving beyond assisting people to taking action. Systems already exist that can use tools, access data, trigger processes, and operate with real permissions.
Level 0 - Room 2.2
Wed 4
16:00h - 17:30h Level 0 - Room 2.2 Public Access
17:00h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Help securing the future. Community projects you can participate in
Mykhailo Sindieiev
Mykhailo Sindieiev DevSecOps Engineer / OWASP Barcelona Leader Speaker
Andrés Galarza
Andrés Galarza AstraZeneca Manager Speaker

2026-11-04 17:00 2026-11-04 18:30 Europe/Madrid Help securing the future. Community projects you can participate in In this session the chapter leaders of OWASP Barcelona give an overview of the community projects, and explain how you can contribute. OWASP is the Open World Application Security Project that drives application security for the software industry. The most well known project is the OWASP TOP 10 but there are hundereds of projects ranging from tools, industry standards and guides. Covering topics such as LLM security, AI agent secutity, supply chain management ,API security, process maturity, cheat sheets and much more. OWASP is a non profit foundation and everything is run by volunteers, you are invited to contribute and turbocharge your carreer in the community of experts. Networking Hub
Wed 4
17:00h - 18:30h Networking Hub Public Access
12:00h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience CISOs & Security Leader IT & Infrastructure

ISC2 Community & Professional Development Forum
Alejandro Cadarso
Alejandro Cadarso ISC2 Spain Chapter / Field CTO President Host
Néstor Angulo
Néstor Angulo ISC2 Spain Chapter / CISSP Head of Technology Moderator
Sebastián Correas
Sebastián Correas ISS & GRC Consultant / CISSP / CCSSP / ISO27001 & ISO 42001 Lead Auditor Speaker
Mykhailo Sindieiev
Mykhailo Sindieiev DevSecOps Engineer / OWASP Barcelona Leader Speaker

#Ciberseguridad, #ISC2, #ISC2Spain, #OWASP, #SBOM

2026-11-04 12:00 2026-11-04 13:30 Europe/Madrid ISC2 Community & Professional Development Forum ISC2 Spain Chapter is organising this 90-minute session to share updates on the Chapter’s development, its certification initiatives, continuing education and professional development activities, and to host a collaborative roundtable with OWASP. The roundtable, entitled “SBOM: The Foundation for Secure Development, Vulnerability Management, and Compliance”, will explore software supply chain security and Software Bills of Materials (SBOMs) in the context of the CRA (Cyber Resilience Act) and NIS2, offering a practical perspective on vulnerabilities and open-source risk management. An open space to learn, exchange experiences and strengthen the professional cybersecurity community. Networking Hub
Wed 4
12:00h - 13:30h Networking Hub Public Access
15:10h
Conference | Hacking Partner Cybersecurity as a strategic business and reputational risk IT & Infrastructure

See NinjaOne in action: Vulnerability remediation in the age of AI-driven exploits
Wladimir Rojo
Wladimir Rojo NinjaOne Team Lead Solutions Engineer for EMEA Speaker

2026-11-04 15:10 2026-11-04 15:35 Europe/Madrid See NinjaOne in action: Vulnerability remediation in the age of AI-driven exploits
What you'll see: Live in NinjaOne, watch a vulnerable application get patched on the spot, an endpoint get hardened against real world attack paths like open USB ports and outdated protocols, and a device recovered from a ransomware style incident using backups, all in a matter of minutes.
Why it matters: Endpoints are now where 90% of cyberattacks originate and where 90% of ransomware incidents begin, with endpoint attacks up 300% quarter over quarter and nearly 40,000 new CVEs published last year alone. This session shows attendees exactly how to close that gap before an attacker gets there first.
Auditorium II
Wed 4
15:10h - 15:35h Auditorium II Full Congress Pass
12:30h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

The dark side of AI: Tackling AI-based cyber attacks
Joan Vives
Joan Vives ManageEngine Technical Consultant Speaker

#AISecurity, #AIThreats, #IdentitySecurity, #PAM, #ThreatLandscape

2026-11-04 12:30 2026-11-04 12:55 Europe/Madrid The dark side of AI: Tackling AI-based cyber attacks Privileged Access Management is evolving beyond simple password vaulting. Discover the mission to turn PAM360 into a comprehensive command center that builds, automates, and orchestrates your entire security landscape. This presentation covers the pillars of a robust PAM framework, the efficiency of automated operations, and the power of complex task orchestration. Auditorium I
Wed 4
12:30h - 12:55h Auditorium I Full Congress Pass
12:30h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

The real story behind zero trust, identity, and device security. From identity to workforce trust: Securing workforce access end-to-end
Darren James
Darren James Specops Software Senior Product Manager Speaker

#AccessControl, #Authentication, #CyberRisk, #DeviceSecurity, #IdentityGovernance, #IdentitySecurity, #WorkforceIdentity, #ZeroTrust

2026-11-04 12:30 2026-11-04 12:55 Europe/Madrid The real story behind zero trust, identity, and device security. From identity to workforce trust: Securing workforce access end-to-end
Workforce access has never been more dynamic or more unpredictable. Users connect from anywhere, on devices that shift daily between personal, managed, trusted, and unknown, and security teams are expected to make the right call every time. Identity tells you who is connecting, but today’s environments make it equally critical to understand what they’re connecting with.
Because if you don’t trust the device, you can’t trust the access. This session explores how identity and device trust come together to meet the real access challenges organizations face. Curious how this story shapes the future of secure access in 2026? Join us to find out.
Auditorium II
Wed 4
12:30h - 12:55h Auditorium II Full Congress Pass
15:10h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

Quantum cryptography: Past, present, future
Carlos Solano Sánchez
Carlos Solano Sánchez NTT Data Senior Product Manager Speaker

#CryptoAgility, #Cryptography, #PostQuantumCryptography, #PQC, #QKD, #QuantumCryptography, #QuantumSecurity

2026-11-04 15:10 2026-11-04 15:35 Europe/Madrid Quantum cryptography: Past, present, future
Cryptography is facing one of the greatest turning points in its history. This presentation will explore the evolution of encryption, from the cryptographic models that currently protect our communications and data to the new paradigms that will shape digital security in the quantum era.
We will analyze the current state of pre-quantum cryptography, the risks posed by the arrival of quantum computers capable of compromising certain existing algorithms, and the transition towards post-quantum cryptography as a response to this new landscape. We will also explore the role of quantum cryptography and technologies such as Quantum Key Distribution (QKD), placing their level of maturity, applications, and challenges into context.
A journey through the past, present, and future to understand how information protection will evolve, what decisions organizations need to start making today, and why crypto-agility will become a strategic capability for addressing the next generation of threats.
Auditorium I
Wed 4
15:10h - 15:35h Auditorium I Full Congress Pass
Thu 05
10:45h
Conference | Congress Systemic, cyber-physical and supply chain resilience IT & Infrastructure

From check-in to takeover: The hidden cyber war on hospitality
Sascha Maier
Sascha Maier SV Group Chief Information Security Officer Speaker

2026-11-05 10:45 2026-11-05 11:10 Europe/Madrid From check-in to takeover: The hidden cyber war on hospitality
Your reservation is at risk. Please re-confirm your card within 24 hours.” It arrives via WhatsApp, with every booking detail correct, and it was written by a criminal.
Hotels, their partners, and booking platforms have quietly become some of the most attractive targets for cybercriminals. Hotels run 24/7 front desks under constant time pressure, have high staff turnover, handle payment data at every touchpoint, and route the guest journey through third-party platforms they don't control. Attackers have industrialised this. They use AI-crafted phishing in guests' own languages, fake “guest complaints” that deliver malware to reception desks, and hijacked extranet accounts that turn trusted channels into fraud machines.
Auditorium II
Thu 5
10:45h - 11:10h Auditorium II Full Congress Pass
11:20h
Conference | Congress Systemic, cyber-physical and supply chain resilience IT & Infrastructure

IoT Security: From device to cloud

Luka Herman
Luka Herman Deutsche Telekom IoT IoT Account Manager Speaker
Abanoub Mouanas Iskandar
Abanoub Mouanas Iskandar Deutsche Telekom IoT Global Account Manager IoT Speaker

2026-11-05 11:20 2026-11-05 11:45 Europe/Madrid IoT Security: From device to cloud
What if someone could turn a supermarket refrigerator into a 50°C oven from the other side of the world? As more devices become connected, securing the device itself is only part of the challenge. The way data travels between the device, network and cloud matters just as much.
This session explores how IoT connectivity can become part of the security architecture. We will look at how private APNs can reduce direct exposure to the public Internet, create controlled communication paths and help ensure that connected devices are reachable where needed, while remaining invisible to everyone else.
Auditorium I
Thu 5
11:20h - 11:45h Auditorium I Full Congress Pass
13:35h
Conference | Congress Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Cold chain, hot target: The OT security opportunity playbook in industrial food and bev sector

Nick Saharan
Nick Saharan CSAFI.ORG President Speaker

2026-11-05 13:35 2026-11-05 14:05 Europe/Madrid Cold chain, hot target: The OT security opportunity playbook in industrial food and bev sector Food processing, wholesale distribution and cold-chain logistics run on the PLCs, SCADA, HMIs and remote access that OT security teams protect every day. NIS2, the CER Directive, the Cyber Resilience Act and PAS 96:2026 are now converging on the sector. Yet most OT security providers struggle to get through the door, because industrial food sector buys differently. Drawing on csafi.org’s work with meat, poultry, dairy and seafood operators across Europe, North America and Australia, this session shows where the risks sit, cyber-physical environment in food manufacturing sector and how to earn a place in the market. Auditorium I
Thu 5
13:35h - 14:05h Auditorium I Public Access
10:05h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

The future of threat intelligence: Defending at machine speed
Staffan Truvé
Staffan Truvé Recorded Future Co-founder & CTO Speaker

2026-11-05 10:05 2026-11-05 10:35 Europe/Madrid The future of threat intelligence: Defending at machine speed As AI changes the speed and scale of cyber threats, intelligence has to evolve with it. This talk explores the changing role of threat intelligence in cyber defense, from identifying emerging risks to turning complex signals into the context needed to act earlier and with greater precision. It will examine how AI and threat intelligence are enabling faster, increasingly autonomous approaches to security, helping defenders keep pace as threats move at machine speed. Auditorium II
Thu 5
10:05h - 10:35h Auditorium II Full Congress Pass
12:30h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

Defending at AI speed

Francisco González Ortiz
Francisco González Ortiz Inetum Microsoft Security Lead Speaker
Gerard Salvador López
Gerard Salvador López Microsoft Global Security Blackbelt Speaker

2026-11-05 12:30 2026-11-05 12:55 Europe/Madrid Defending at AI speed Cyber threats evolve rapidly and security operations must adapt to respond just as fast. This session explores the key challenges, needs, and capabilities for enabling an AI assisted cyberdefense model that accelerates detection, investigation, and response. Attendees will gain insights into how organizations can foster human expertise with AI capabilities to improve their chances to stay ahead of increasingly sophisticated attacks. Auditorium II
Thu 5
12:30h - 12:55h Auditorium II Full Congress Pass
11:00h
Side Event | Side Event AI, identity and trust in the digital environment IT & Infrastructure

The cyber-AI paradox: Why research must simultaneously advance AI-based defense and secure the AI pipeline
Shuaib Siddiqui
Shuaib Siddiqui Cybersecurity & Blockchain Research Group Director Speaker
Josep Pegueroles
Josep Pegueroles UPC-ETSETB Professor Speaker
Pere Tuset-Peiró
Pere Tuset-Peiró Professor of Computer Networks & Cybersecurity Speaker

2026-11-05 11:00 2026-11-05 12:30 Europe/Madrid The cyber-AI paradox: Why research must simultaneously advance AI-based defense and secure the AI pipeline
Artificial Intelligence is rapidly transforming cybersecurity, providing new capabilities to detect threats, automate analysis, and respond to increasingly sophisticated attacks. At the same time, the growing adoption of AI introduces a new and complex attack surface: the AI pipeline itself.
This dual challenge—the Cyber-AI paradox—is at the core of the research carried out by GREC, the Cognitive Cybersecurity Research Group, which brings together researchers from i2CAT, UPC, and UOC. The group approaches AI and cybersecurity from two complementary directions: using AI to strengthen cyber defense, while simultaneously ensuring that AI systems and their entire pipelines are secure, trustworthy, and resilient.
During the session, we will present the main research lines currently being explored by GREC and showcase some of the work carried out in these areas, ranging from AI-driven approaches for threat detection and cyber defense to the identification and mitigation of security risks affecting AI models, data, and infrastructures.
The talk will provide an overview of the challenges, ongoing research, and lessons learned at the intersection of AI and cybersecurity, highlighting why advancing AI-based defense and securing the AI pipeline must be addressed together to build the next generation of resilient digital infrastructures.
Networking Hub
Thu 5
11:00h - 12:30h Networking Hub Public Access
13:35h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

From alert fatigue to autonomous triage: How agentic AI is reshaping vulnerability management
Sharjeel Qayyum Khan
Sharjeel Qayyum Khan EPAM Systems Senior Enterprise Security Architect (EMEA) Speaker

2026-11-05 13:35 2026-11-05 14:00 Europe/Madrid From alert fatigue to autonomous triage: How agentic AI is reshaping vulnerability management Security teams are drowning in findings. SAST, SCA and secret-scanning tools generate thousands of alerts, most of them false positives or unreachable code, and analysts spend more time sorting noise than fixing real risk. This session shows how agentic AI can change that. Drawing on a working system I designed and built, I will walk through how an AI triage pipeline combines retrieval over CWE, MITRE ATT&CK and CISA KEV knowledge, code reachability analysis and exploit-probability scoring to classify findings, explain its reasoning and route confirmed issues straight to developers as fix pull requests, with a human analyst kept in the loop for every decision. Attendees will leave with a practical architecture, the guardrails that make AI triage trustworthy, and an honest view of where it works and where it still needs people. Auditorium II
Thu 5
13:35h - 14:00h Auditorium II Full Congress Pass
13:05h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

A sign without a lock: How the web decides which AI Agents to trust
Jaime Morales Rodríguez de Lope
Jaime Morales Rodríguez de Lope Lognext Head of Cybersecurity Speaker

2026-11-05 13:05 2026-11-05 13:30 Europe/Madrid A sign without a lock: How the web decides which AI Agents to trust
AI agents no longer just answer questions. They browse, read and act on online services on our behalf. Every website now faces a new decision: trust this automated traffic, restrict it, or block it.
This talk presents the results of an empirical study on how websites actually treat AI-related User Agents. Combining large-scale measurement with controlled testing, we compared what websites declare in their policies, such as robots.txt, with what they really enforce. We also examined whether they identify AI agents, apply differentiated rules, and penalize some agents more than others.
The results show a fragmented and immature ecosystem. Some AI agents are widely accepted, while others face significantly more restrictions and blocking. In many cases, declared rules and real enforcement do not match. Together, these patterns point to new forms of trust and reputation between websites and autonomous systems.
Attendees will leave with a clear view of how the Internet is adapting to AI-driven traffic, which agents are penalized most often, and what this means for security, for businesses that publish content, and for the future of machine-to-web communication.
Auditorium II
Thu 5
13:05h - 13:30h Auditorium II Full Congress Pass
12:00h
Side Event | Side Event AI, identity and trust in the digital environment IT & Infrastructure

Las vulnerabilidades que no te quita la IA

2026-11-05 12:00 2026-11-05 13:00 Europe/Madrid Las vulnerabilidades que no te quita la IA La IA está cambiando la forma de realizar auditorías y Bug Bounty, pero hay vulnerabilidades que siguen requiriendo algo que ningún modelo puede automatizar por completo: experiencia, creatividad y una comprensión profunda del comportamiento de una aplicación. En esta charla nos olvidaremos de los fallos más comunes que la IA ya es capaz de encontrar y nos centraremos en bugs concretos y poco convencionales que todavía requieren una mirada humana. A través de mi experiencia con docenas de vulnerabilidades reportadas antes y después de la llegada de la IA, veremos cómo la especialización puede convertirse en una ventaja frente a otros hackers y frente a la propia inteligencia artificial. Analizaremos ejemplos reales de vulnerabilidades y técnicas de explotación que he encontrado en auditorías y programas de Bug Bounty, y cómo desarrollar una metodología para descubrir aquello que otros pasan por alto. Level 0 - Room 2.1
Thu 5
12:00h - 13:00h Level 0 - Room 2.1 Public Access
11:00h
Side Event | Side Event Cybersecurity as a strategic business and reputational risk IT & Infrastructure

Return of Sedinho: Current situation and new tactics of the Brazilian banking trojan ecosystem

2026-11-05 11:00 2026-11-05 12:00 Europe/Madrid Return of Sedinho: Current situation and new tactics of the Brazilian banking trojan ecosystem During several years we have been tracking the evolution of Brazilian banking trojans, their expansion into countries well beyond their original sphere of influence, and the law enforcement operations that attempted to disrupt their activity. Building on that work, this talk revisits the current landscape and examines the latest improvements and changes introduced by the malware operators behind these groups. In this session, we will analyze several recent financially motivated campaigns that show how Latin American threat actors are not only evolving classic banking malware, but also introducing NFC based mobile fraud against victims in multiple countries. We will provide concrete examples of how well known families such as Grandoreiro and Casbaneiro are refining both their techniques and their social engineering narratives while continuously adapting their malware infection chains and evasion strategies. We will also introduce their newest Android campaigns that leverage NFC fraud through a new NGate variant that masquerades as legitimate applications intended to relay NFC card data between devices. Cybercriminals distribute these trojanized apps under various pretexts, including online banking tools, lottery apps, and shopping applications. Once installed, the malware intercepts NFC payment card data and the victim's PIN, forwarding them to attacker controlled infrastructure to enable contactless ATM cash outs and fraudulent POS transactions, all without requiring additional risky permissions. Throughout the talk, we will walk through the observed tactics, techniques, and procedures, highlighting how the malware code, supporting infrastructure, and social engineering patterns have changed compared to the campaigns we analyzed previously. Our goal is to raise awareness of the ongoing evolution of these Latin American originated malware operations and to equip security teams with the context they need to detect and block these threats before they can cause damage to their organizations. Level 0 - Room 2.1
Thu 5
11:00h - 12:00h Level 0 - Room 2.1 Public Access
10:00h
Side Event | Side Event Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Breaking trust: Internal desktop apps and the AppStream illusion

2026-11-05 10:00 2026-11-05 11:00 Europe/Madrid Breaking trust: Internal desktop apps and the AppStream illusion
Desktop applications have fallen out of the spotlight in the AI era, yet they remain deeply embedded in the internal infrastructure of countless companies and research labs, often running with elevated trust and minimal scrutiny.
This talk examines the security posture of desktop applications through the lens of Tier2 vs. Tier3 architectures, breaking down the structural weaknesses inherent to each model. Through real-world case studies, we'll walk through practical exploitation of common vulnerability classes (including login bypass, authentication bypass, and insecure deserialization), demonstrating how these flaws are found and abused in production environments.
We'll then examine standard remediation strategies for these vulnerabilities and discuss their inherent limitations. Finally, we'll dig into a widely adopted mitigation pattern: using application virtualization platforms like AppStream or Citrix to "convert" a Tier2 application into a Tier3-equivalent deployment.
We'll critically assess whether this approach constitutes a genuine architectural fix. Spoiler: it doesn't always hold up, and we'll show how it can be bypassed.
Level 0 - Room 2.1
Thu 5
10:00h - 11:00h Level 0 - Room 2.1 Public Access
12:30h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

Cutting through the HYPE: A practical approach to secure AI adoption
Federico Teti
Federico Teti Zscaler Principal Strategy Architect Speaker

2026-11-05 12:30 2026-11-05 12:55 Europe/Madrid Cutting through the HYPE: A practical approach to secure AI adoption In this session, we cut through the noise and hype surrounding AI security to explore a practical, reality-based approach for secure AI adoption in the enterprise. While many vendors market broad AI security promises, they are often built on legacy architectures that fail to address decentralized agents and runtime risks. We will examine Zscaler's Zero Trust approach to AI security, demonstrating how true visibility, inline safeguards, and agent governance deliver real protection and risk mitigation beyond market rhetoric. Auditorium I
Thu 5
12:30h - 12:55h Auditorium I Full Congress Pass
13:05h
Conference | Congress Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Cyber resilience of emergency coordination centres from a law enforcement perspective on European security research
Rubén Fernández Bleda
Rubén Fernández Bleda Ajuntament de València Police Officer and Project Manager Speaker
José L. Diego
José L. Diego Ajuntament de València Police Inspector and Chief of Staff to the Chief Commissioner Speaker

#CriticalInfrastructure, #CyberResilience, #IncidentManagement, #LawEnforcement, #PublicSafety, #SecurityOperations

2026-11-05 13:05 2026-11-05 13:30 Europe/Madrid Cyber resilience of emergency coordination centres from a law enforcement perspective on European security research
This presentation explores how EU-funded security research helps law enforcement agencies protect citizens and counter cybercrime, from defining operational needs and co-designing solutions to validating emerging technologies.
Drawing on València Local Police’s experience, it focuses on the GANNDALF pilot protecting the city’s emergency coordination centre, including its 092 call line and dispatch services. The pilot tests tools for early threat detection, cyber risk assessment, forensic visualisation and decision support against phishing, ransomware-style disruption and denial-of-service scenarios.
Using simulated environments and synthetic data, the session examines how an emergency organisation can safely evaluate advanced cybersecurity tools. It shares practical lessons on collaboration between police, researchers and technology providers, bridging European security R&D with the everyday operational needs of public safety agencies,
Auditorium I
Thu 5
13:05h - 13:30h Auditorium I Full Congress Pass
10:45h
Conference | Congress AI, identity and trust in the digital environment IT & Infrastructure

Who governs the agents? Identity governance in the age of agentic AI
Raul D'Opazo
Raul D'Opazo One Identity Solutions Architect Speaker

#AccessControl, #AIAgents, #AISecurity, #Authorization, #IdentityGovernance, #NonHumanIdentities, #ZeroTrust

2026-11-05 10:45 2026-11-05 11:10 Europe/Madrid Who governs the agents? Identity governance in the age of agentic AI AI agents are rapidly becoming autonomous actors within the enterprise: accessing applications, consuming APIs, handling data and making decisions on behalf of humans and organisations. But who owns these identities? Who grants their access, certifies their permissions and removes them when they are no longer needed? This session explores why Agentic AI requires us to extend Identity Governance beyond the human workforce. We will examine how AI agents can be discovered, assigned ownership, governed throughout their lifecycle and linked to the permissions they accumulate across cloud and enterprise environments. The goal is simple: enable organisations to embrace Agentic AI without losing control of who - or what - has access to what, why, and on whose behalf. Auditorium I
Thu 5
10:45h - 11:10h Auditorium I Full Congress Pass
11:55h
Conference | Congress Systemic, cyber-physical and supply chain resilience IT & Infrastructure

Securing the intelligent network: Cyber resilience for AI, 5G and 6G
Connie McIntosh
Connie McIntosh Ericsson Head of Security Speaker

#5GSecurity, #6GSecurity, #AISecurity, #CriticalInfrastructure, #CyberResilience, #NetworkResilience, #NetworkSecurity, #TelecomSecurity

2026-11-05 11:55 2026-11-05 12:20 Europe/Madrid Securing the intelligent network: Cyber resilience for AI, 5G and 6G AI is transforming intelligent transport networks into autonomous, software-defined systems, but with greater autonomy comes greater risk. This session examines emerging cyber threats across AI-driven control planes, edge and satellite infrastructure, quantum disruption, and the intersection of EU sovereignty, EU regulation, and cyber resilience. Auditorium I
Thu 5
11:55h - 12:20h Auditorium I Full Congress Pass
Close